Service

Active Directory Security Audit
Active Directory Audit, test and audit AD, ransomware defense, second line of defense

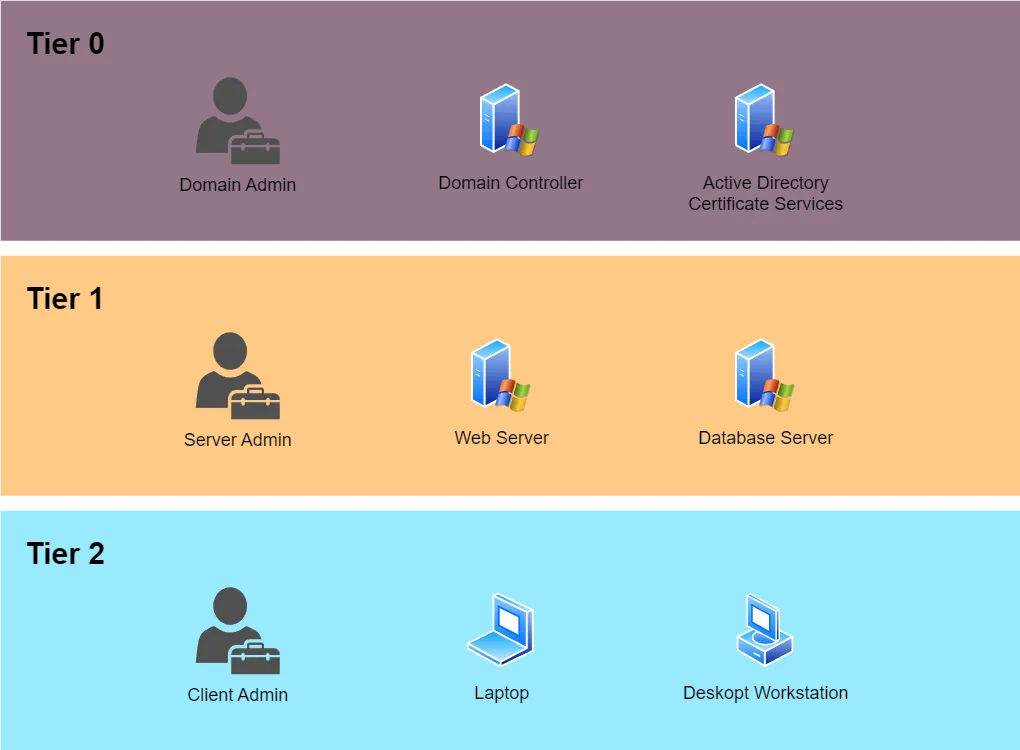
An Active Directory Audit is a white-box security assessment of your on-premises Active Directory that identifies misconfigurations, dangerous permissions, and attack paths leading to domain takeover, before an attacker or ransomware can exploit them.

The ransomware attacks with the biggest impact run through Active Directory: whoever takes over the domain controls every system and every file in the company. A single forgotten permission or an old misconfiguration is often all it takes. These are exactly the vulnerabilities this audit uncovers, before an attacker finds them.
Internal IT Infrastructure Penetration Test

Internal penetration test, test internal IT infrastructure, ransomware prevention

An Internal IT Infrastructure Penetration Test simulates an attacker who already has a foothold inside your network (for example after a phishing click) and tests whether they can move laterally and reach Domain Admin.

Someone on your team clicks the wrong email attachment, and an attacker is inside your network. What happens next depends on what they find there: does the attack stop at one machine, or do they move laterally and take over every system you run? This test answers that question before a real attacker does.

Cloud Infrastructure Security Audit

Cloud Infrastructure Audit, Azure, AWS configuration review, IAM, cloud security

A Cloud Infrastructure Audit is a read-only, white-box review of your Azure, AWS, or GCP environment that finds misconfigurations, over-privileged IAM roles, and exposed services before attackers do.

Cloud services offer enormous flexibility, but that flexibility comes with risk. Misconfigured storage buckets, overly permissive IAM roles, and exposed management interfaces are among the most common causes of cloud security incidents. A Cloud Infrastructure Audit reviews your cloud environment with a read-only account to identify exactly these issues before attackers do.

Supported platforms: Azure, AWS, and GCP. For Azure environments, cloud IAM misconfigurations are frequently intertwined with Entra ID role assignments and Conditional Access; both are often reviewed together.

Cyber Attack Simulation

Cyber attack simulation, red team, attack detection, response testing

A Cyber Attack Simulation recreates realistic, end-to-end attack scenarios to test whether your people, processes, and security tools actually detect and respond to an attacker who is already inside.

Also called an attacker simulation or adversary simulation.

Realistic attack scenarios and typical attack paths are recreated to validate how well your organization can detect and respond to real-world attacks. A penetration test finds vulnerabilities in systems. A cyber attack simulation tests whether your people, processes, and tools actually catch an attacker who is already inside.

Entra ID Security Audit

EntraID Audit, Azure AD / Microsoft Entra ID configuration review, identity management

An Entra ID Audit (formerly Azure AD) is a white-box review of your Microsoft Entra ID tenant that uncovers identity and access misconfigurations, weak Conditional Access policies, and privilege escalation paths.

EntraID (Microsoft Entra ID) is Microsoft’s central identity and access management (IAM) solution, especially in Microsoft 365 environments, and forms the basis for single sign-on (SSO) and access control. A misconfiguration can lead to unauthorized access to company resources or facilitate social engineering attacks. Therefore, this component must be thoroughly tested.

External IT Infrastructure Penetration Test

External penetration test, test external IT infrastructure and attack surface

An External IT Infrastructure Penetration Test assesses your internet-facing systems (servers, VPNs, mail, remote access) for exploitable vulnerabilities and exposure that an attacker could use to gain a foothold.

If your system is exposed to the internet, it could potentially be hacked by anyone. Okay, I exaggerate a bit, but I think you understand. Vulnerabilities in your external infrastructure can lead to very bad press and threaten your customers’ personal information. Regular external infrastructure penetration testing keeps that attack surface in check.

Microsoft 365 Audit

Microsoft 365 Audit, M365 security review, Exchange Online, Teams, SharePoint, Defender

A Microsoft 365 Audit is a read-only, white-box review of your M365 tenant (Exchange Online, Teams, SharePoint, Defender, and admin roles) that finds misconfigurations enabling phishing, data theft, or account takeover.

Microsoft 365 is the productivity backbone of most modern organizations: Exchange Online handles email, Teams drives collaboration, SharePoint stores documents, and Entra ID manages identities. A misconfiguration in any of these components can expose sensitive data, enable phishing attacks, or allow unauthorized access to company resources.

Security Awareness Training

Security Awareness Training, staff training phishing, social engineering, passwords

Security Awareness Training teaches your staff to recognize and resist the attacks that cause most breaches: phishing, social engineering, and weak passwords, delivered by a pentester who actually runs these attacks.

Most cyber attacks begin with a human error. Someone has set a weak password or opened the wrong email attachment. Therefore, it is essential that all employees are trained on how to behave correctly.

Web Application Penetration Test

Web Application Penetration Test, test web apps for vulnerabilities, OWASP

A Web Application Penetration Test is a manual security assessment of a web application and its APIs, focused on the OWASP Top 10: broken access control, injection, authentication flaws, and business logic vulnerabilities.

Your web application is reachable from the internet around the clock, for your customers and for attackers alike. A single access control flaw is often enough to expose other users’ data or take over the server. Those are exactly the flaws I find, before someone exploits them.